Govern the operations around banking before control breaks after the fact
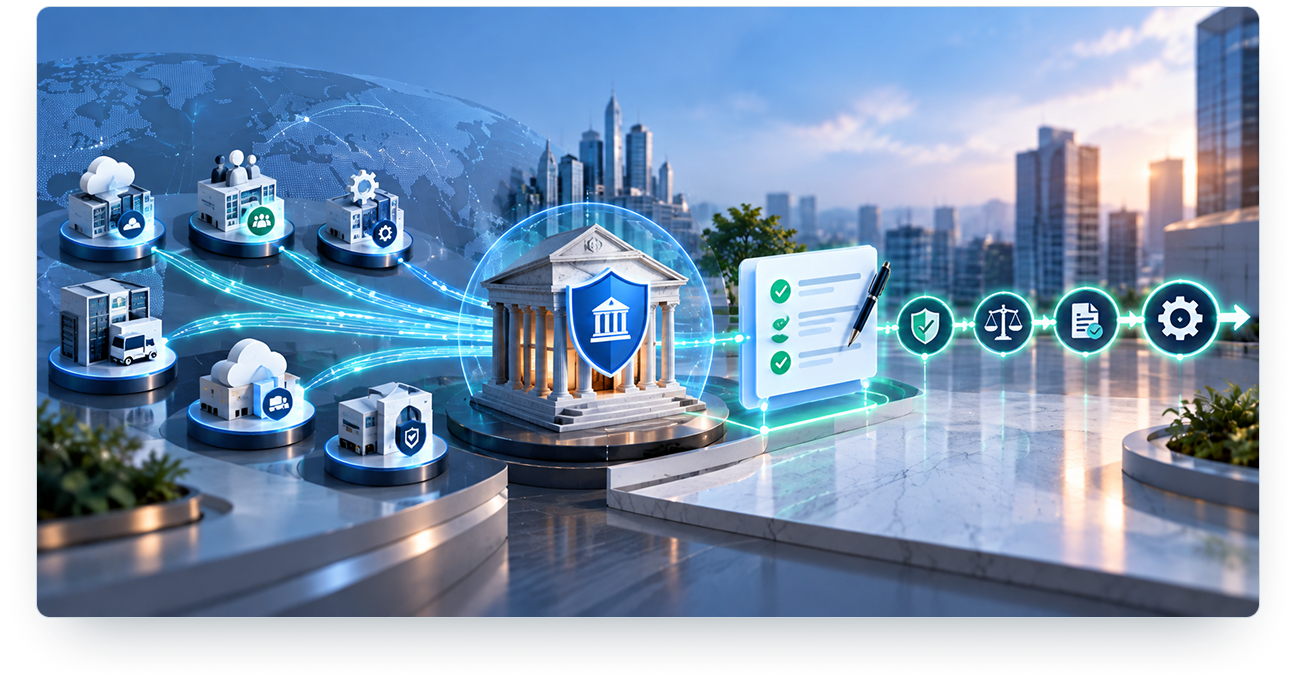
ZoikoSuite connects finance, workforce, legal, third-party, compliance-obligation, evidence and decision workflows across banking entities and jurisdictions — so material internal actions can move with policy, authority and auditability built in.
What does ZoikoSuite do for banks?
ZoikoSuite is a governance-first enterprise operations layer that sits around existing banking systems. It governs the internal operating actions that create risk, accountability, evidence and regulatory exposure — finance, workforce, legal and third-party, obligations, approvals and evidence — across banking entities and jurisdictions. The banking core and specialist risk systems remain external systems that ZoikoSuite integrates with or receives context from.
The banking core may be controlled. The operations around it are often fragmented.
Five operating conditions, each paired with the executive exposure it creates. No percentages, regulatory claims or savings figures.
Multi-entity fragmentation
Finance, workforce, contracts, obligations, evidence and approvals sit in separate systems across legal entities and business units.
Reconciliation overhead, weak ownership, inconsistent control, delayed executive visibility.
Policy outside the action
Authority, policy, legal review and compliance checks may occur in email, spreadsheets, tickets — or after execution.
Control failures discovered too late and difficult decision reconstruction.
Obligation ownership gaps
Regulatory, contractual, tax, workforce, vendor and corporate obligations can be tracked separately.
Missed ownership, duplicate work, late escalation, weak evidence.
Evidence reconstruction
Approvals, rule basis, source records, documents and system events must be assembled during audit or investigation.
Slow assurance, fragile audit narratives, costly evidence retrieval.
Integration sprawl
Core banking, finance, HR, legal, procurement, identity and specialist risk tools exchange data through fragmented integrations.
Unclear data ownership, vendor risk, lineage gaps, technical debt.
ZoikoSuite surrounds the core — it does not replace it
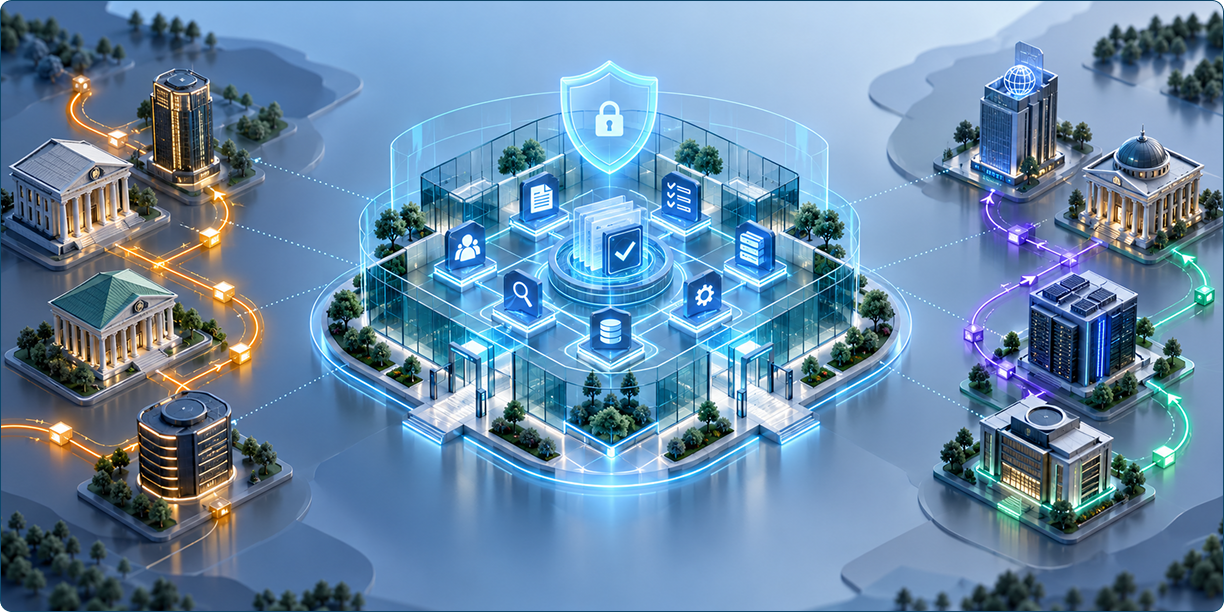
External banking systems stay visually and architecturally distinct. What ZoikoSuite governs is the internal operating action, not the customer transaction.
Eight domains, each with its proof surface
Validated ZoikoSuite domains mapped to banking enterprise jobs. Every capability carries a claim status.
Finance & tax
Maintain entity-aware financial truth, governed approvals, close context, tax treatment and reconciliation evidence.
Ledger and close status, exception queue, approval lineage, Shadow Ledger comparison.
Workforce & payroll
Govern employment and pay processes across branches, entities, jurisdictions and worker types.
Payroll explainability, worker and entity context, approval and exception history, effective-dated policy.
Legal & commercial
Move vendor contracts, authority, clauses, obligations, approvals and spend through controlled execution.
Contract status, signatory authority, clause-linked obligations, vendor diligence, decision history.
Compliance & obligations
Know what operational obligation is due, why it exists, who owns it, and what evidence supports completion.
Obligation registry, due dates, owner, entity and jurisdiction, escalation, evidence status. Not AML/KYC or prudential reporting.
Evidence & audit
Retrieve complete decision, workflow, document, event and evidence lineage.
Audit timeline, evidence manifest, integrity status, controlled export.
Intelligence & reporting
Prioritize operational risk and forecast exposure without changing authoritative source truth.
Anomaly queue, scenario and context, confidence, human-review boundary, executive reporting.
Security & sovereign trust
Apply identity, segregation of duties, encryption, service trust, deployment, residency and telemetry principles.
Status-labeled controls with trust and resource links.
Integration & migration
Connect existing systems and adopt progressively without a big-bang core replacement.
API and event health, provenance, mapping, migration integrity, parallel-run evidence.
Context resolves before a decision is offered
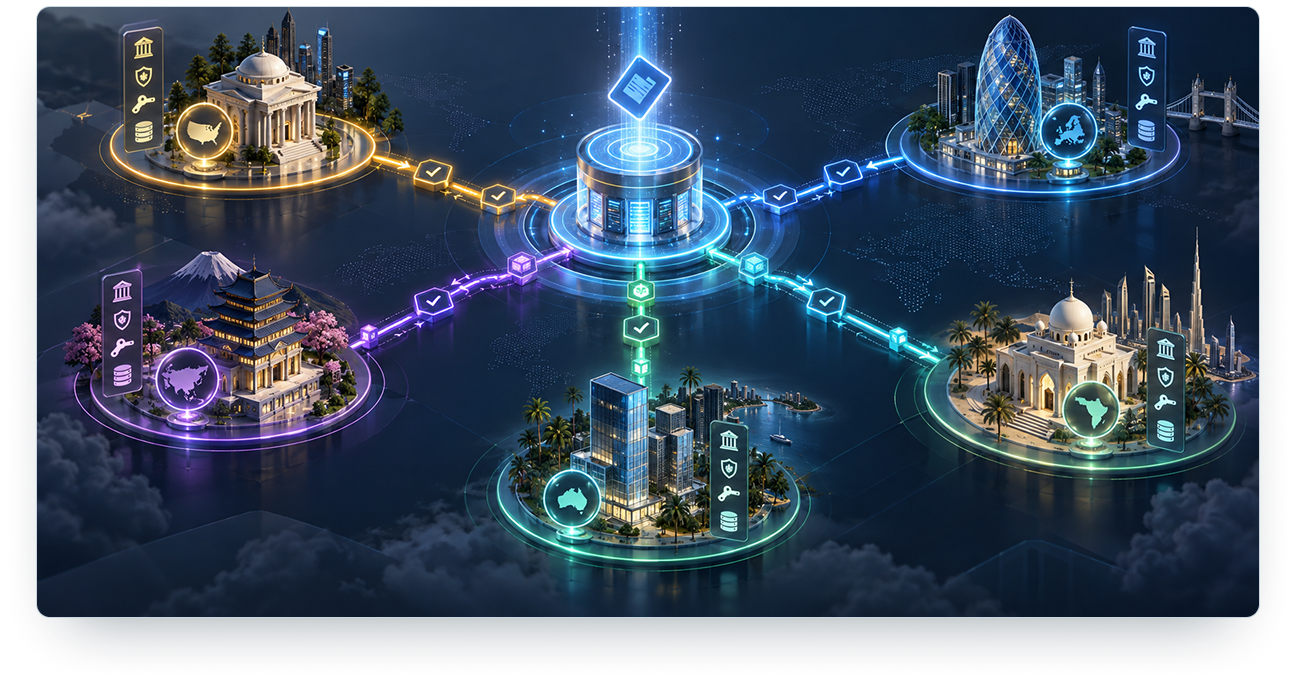
A banking group's entities differ in jurisdiction, authority scheme and residency position. Each is resolved per action rather than assumed from a group default.
Prove the control operated — not merely that an obligation existed
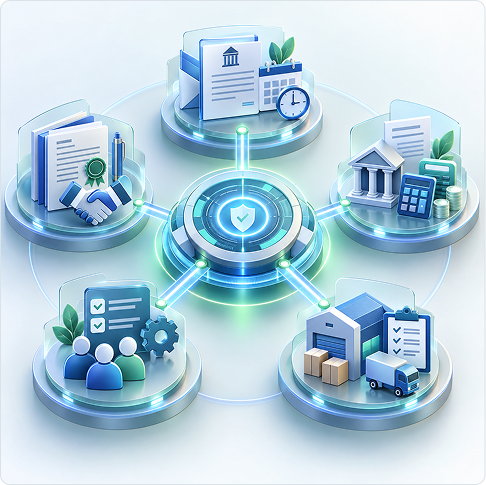
Operational obligations only: regulatory correspondence deadlines, contractual commitments, tax filings, workforce and vendor duties. Not AML/KYC casework or prudential returns.
Governance decision
Actor, entity, jurisdiction, policy basis, authorization outcome, timestamp.
Workflow history
Every transition, approver, delegation, rejection, escalation and rationale.
Document lineage
Version, integrity hash, access history, signature status, retention.
Operational event
Typed event, source service, object, actor or principal, correlation.
Evidence manifest
Scenario-specific package with controlled export.
Integrity controls
Append-only records and tamper-evident chains, with cryptographic validation where implemented.
Signatory authority is checked before execution, not after
Third-party risk is a supervisory focus for banks. This is the contract and vendor path with authority in the execution route.
Bank-grade diligence without overclaiming certification
Each control tile states whether it is an architecture requirement, a stated implementation status, a roadmap item or partner-supported.
Zero-trust access
Identity-verified access with no implicit network trust.
Segregation of duties
Preparer, reviewer, approver and executor independently permissioned.
Workload identity
Service principals are named actors in the evidence record.
Encryption in transit and at rest
Stated per deployment rather than as a universal claim.
Customer-managed keys
Depends on deployment option and approved region.
Region-aware residency
A primary storage region does not imply every lifecycle stage stays in region.
Independent certification
The control framework exists. No SOC, ISO or PCI certification is claimed.
Sovereign deployment
Not currently available. Requirements can be discussed with an architect.
Penetration testing
Conducted through approved partners; reports available under agreement.
System boundaries, stated explicitly
The most common banking objection is replacement risk. The answer is a boundary table, not a reassurance.
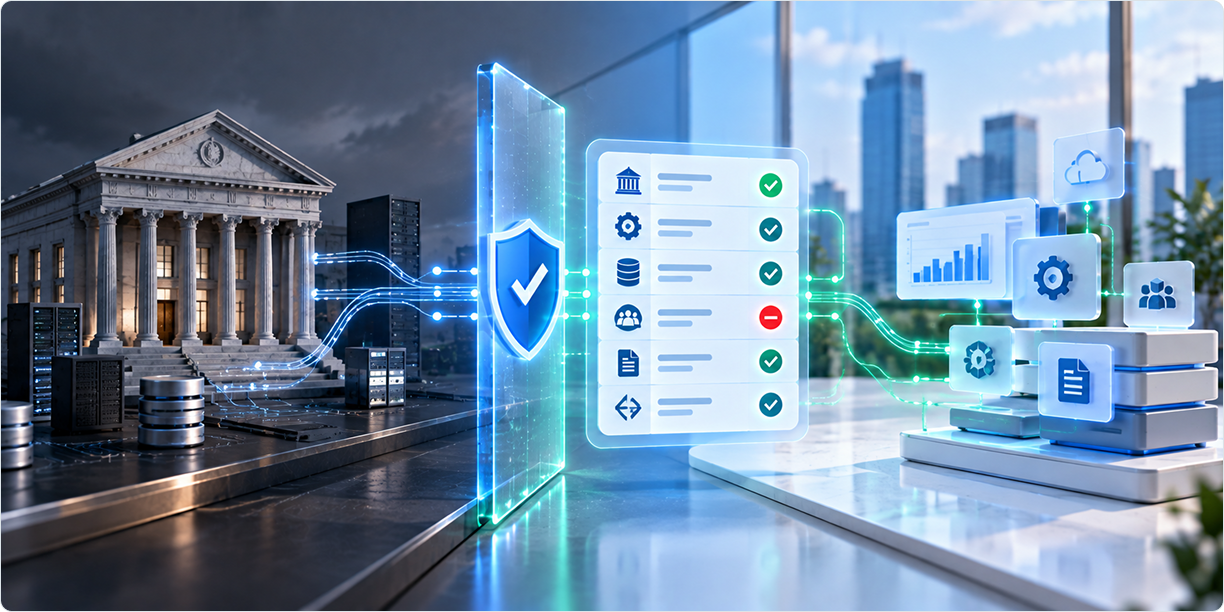
Bounded, and stated as two lists
In a banking context the boundary matters more than the capability. Both lists are published rather than summarized as a reassurance.
AI MAY
- Prioritize operational exceptions for human review
- Detect anomalies against configured operating expectations
- Forecast operational exposure, labelled as a projection
- Suggest reconciliation matches for a human to confirm
- Summarize a decision basis with sources cited
- Flag an obligation or control that appears to need attention
AI MAY NOT
- Approve, authorize or execute any operating action
- Alter authoritative source truth in any system
- Perform or influence AML, sanctions, fraud or credit decisions
- Determine accounting treatment, tax position or capital treatment
- Mark an obligation, control or close dependency as satisfied
- Substitute for legal, tax, accounting, audit or regulatory judgment
Seven stakeholders, one control model
Each buying stakeholder sees the same governed action from their own accountability position.
Financial truth and entity accountability
Entity-aware finance, close status, governed approvals, exception evidence, Shadow Ledger comparison.
Operational control across functions
Obligation queues, approvals, ownership, escalations, integration health, status views.
Obligation ownership and evidence
Rule and obligation basis, entity and jurisdiction context, due dates, escalation, evidence manifests.
Authority and legal execution
Contract lineage, signatory rules, clause obligations, delegated authority, decision history.
Workforce and payroll governance
Worker and entity context, effective-dated policy, payroll explainability, exception controls.
One governed control and integration model
APIs and events, workload identity, segregation of duties, encryption and residency labels, deployment options.
Evidence that the control operated
Decision basis, workflow history, document lineage, operational events. Read-only by default, with no operational approval authority.
Governance Platform
- Governance Platform
- Authority and segregation
- Core modules
Platform Foundation
- Platform Foundation
- Deployment options
- Migration & Shadow Mode
Financial Service
- Financial Service
- Solve Critical Challenges
- Organization Type
CFOs
- CFOs
- General Counsel
- Leadership teams
Not published
No approved banking customer story exists. No anonymised composite, representative outcome or unnamed "tier-1 bank" reference is substituted.
No regulated legal, tax, accounting, audit or prudential advice is provided.
No supervisory approval, capital treatment, compliance certification or regulatory outcome is determined or guaranteed.
Bring the internal action your auditors asked you to reconstruct
A vendor contract signed without the second signature. An obligation that escalated late because nobody owned it. A payroll release approved outside the local mandate. We will trace one through context, authority and evidence against your own entity and jurisdiction structure.
No capability availability, jurisdiction coverage, residency option, certification, supervisory approval or regulated outcome is committed outside an approved commercial document.
Book enterprise demo
Every section of this page was readable without it.
Scope, coexistence, certification and boundaries
Direct first sentences, then qualified detail. Every answer is present in the page source.
No. It is a governance-first enterprise operations layer that sits around existing banking systems.
Account processing, deposit servicing, loan origination or servicing, payments processing, transaction banking, and card issuing or acquiring are not claimed and not implied by any interface element.