Govern obligations. Preserve evidence. Prove the control operated.
ZoikoSuite is architected to connect obligations, policy, ownership, approvals, jurisdiction context, exceptions and evidence across governed business operations. Coverage and assurance are published by status — never as blanket claims.
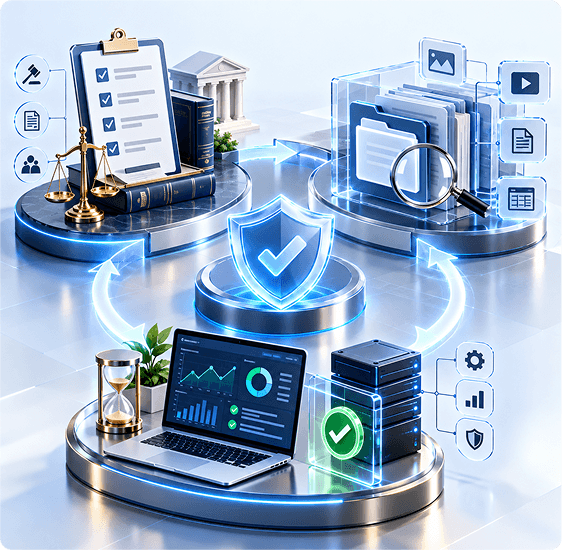
From obligation to evidence, in seven steps
Know what is due, why it is due, who owns it, and what evidence exists — with the decision governed before execution rather than documented afterwards.
Obligation identified
Source, basis and effective date recorded with provenance.
Applicability resolved
Entity, jurisdiction and workflow scope determine whether it applies.
Owner assigned
A named person, never a team alias, with an escalation path.
Policy applied
Controlling rule with version and effective date attached.
Human decision
Approve, defer or raise an exception — by an accountable person.
Execution or filing
Performed in the approved system of record, commonly not ZoikoSuite.
Evidence preserved
Decision basis and lineage retained as the work happens.
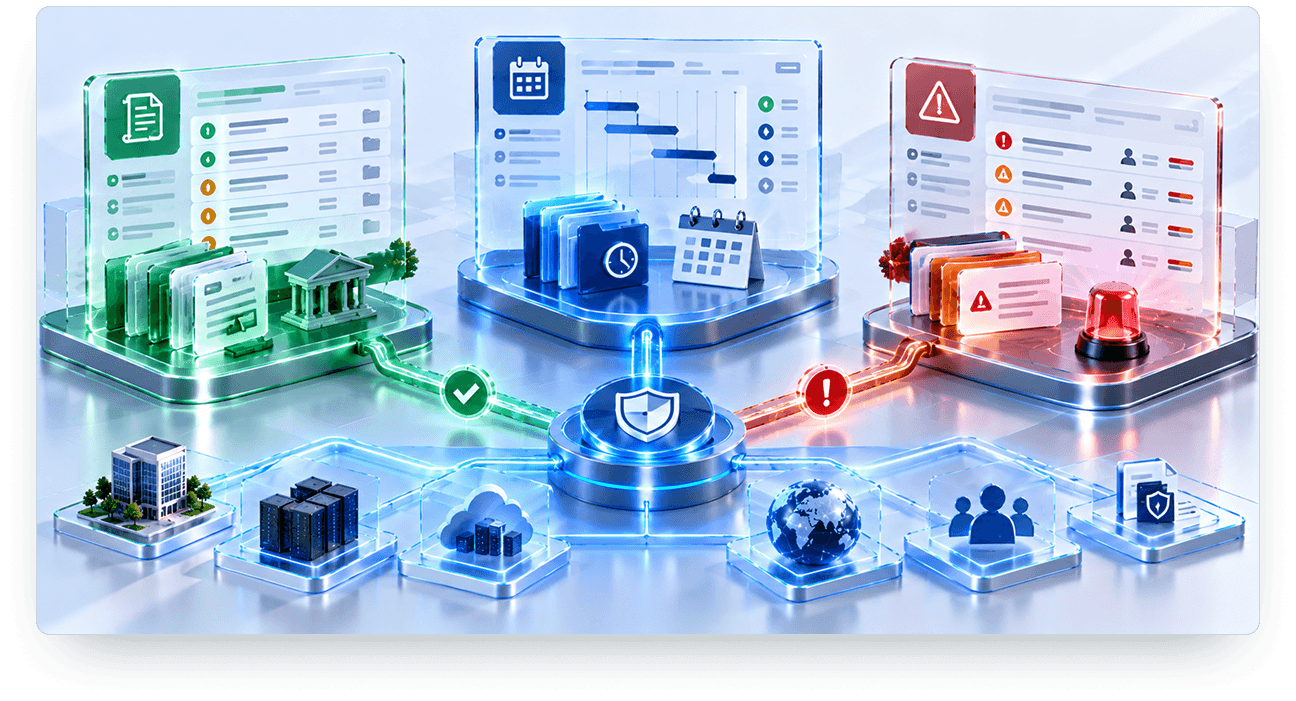
Registry, owners, escalation and evidence
The named proof surfaces: obligations registry, filing tracker and escalations. Synthetic data throughout.
Coverage is published per workflow, with a review date
Five states, each carrying workflow scope, last-reviewed date and provenance. A jurisdiction is never marked covered as a whole.
United Kingdom
AvailableGermany
LimitedSingapore
Partner-supportedUnited States
Needs reviewMapping is a relationship.
Assurance is a verdict.
These are different things, and conflating them is the most common way a compliance page misleads. They are kept visually and structurally separate here.
A stated relationship between ZoikoSuite's control model and a framework's control objectives. It describes design intent and alignment.
- •Produced internally by ZoikoSuite
- •Describes how a control addresses an objective
- •Useful input to your own assessment
- •Can be shared and discussed
- •Updated as the product changes
A verdict from a qualified third party that controls operated effectively over a defined period, for a defined scope.
- •Requires an external verifier
- •Requires a stated scope and period
- •Requires a current status and date
- •None currently exists for ZoikoSuite
- •No badge or logo appears until it does
Access control
Identity, role, attribute, entity scope, delegation and segregation of duties mapped to access-control objectives.
Change management
Authority evaluation, approval path, exception handling and expiry mapped to change-control objectives.
Audit logging & monitoring
Decision records, workflow history and access events mapped to logging and monitoring objectives.
Risk & obligation management
Obligation registry, ownership, escalation and review cadence mapped to risk-management objectives.
Evidence & records
Six-layer evidence model and manifest export mapped to records and evidence objectives.
Third-party management
Vendor register, diligence tracking and dependency exposure mapped to third-party objectives.
Six layers, with an export path
Evidence Architecture owns the depth. This is the summary a compliance reviewer needs to decide whether to go further.
Governance decision
Actor, entity, jurisdiction, policy basis, authorization outcome, timestamp.
Workflow history
Every transition, approver, delegation, rejection, escalation and rationale.
Document lineage
Version, integrity hash, access history, signature status, retention reference.
Operational event
Typed event, source service, object, actor or principal, correlation.
Evidence manifest
Scenario-specific package with controlled export and its own access record.
Integrity controls
Append-only records and tamper-evident chains, with cryptographic validation where implemented.
An exception without an expiry is just a policy change nobody approved
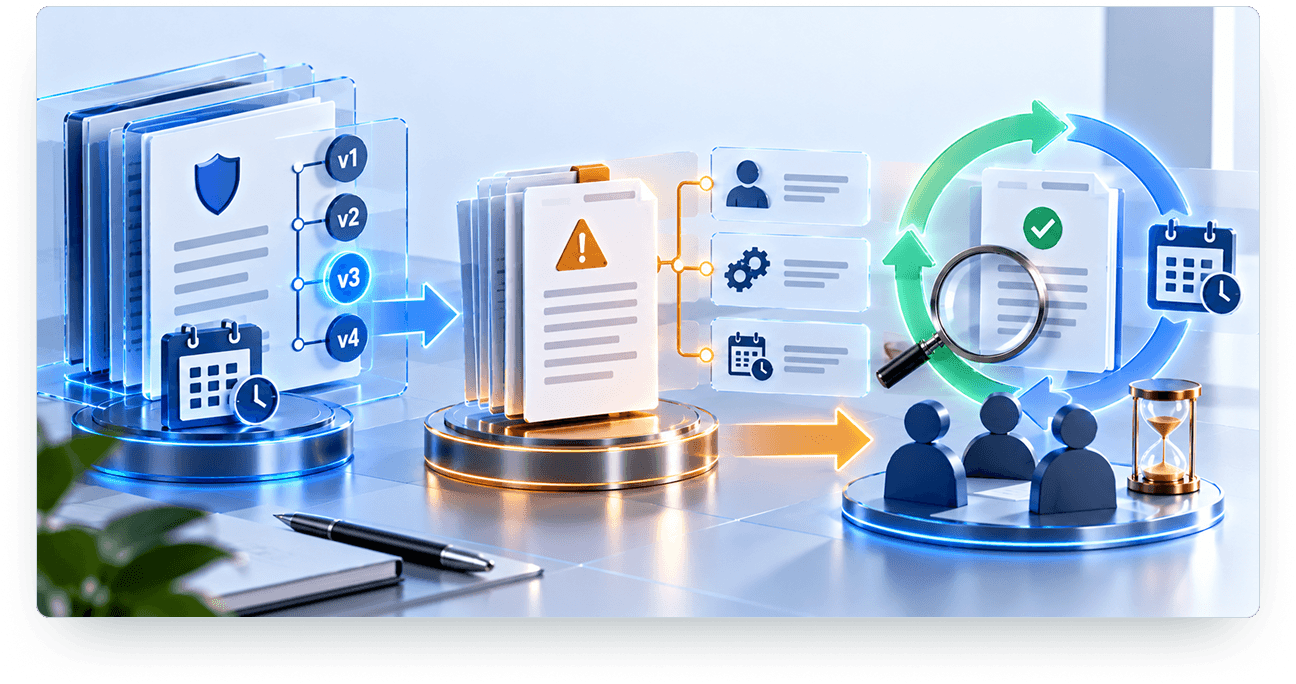
Policies carry versions and effective dates. Exceptions carry owners, compensating controls and expiry dates, and reappear for decision rather than lapsing into permanent practice.
What exists, what does not, and who owns the depth
This page does not duplicate the other Trust destinations. Each owns its own subject, and destinations that are not yet published are marked rather than linked.
None currently
No SOC, ISO, HITRUST, FedRAMP, StateRAMP or equivalent certification or attestation is currently held. No badge or logo appears anywhere, and none will until a verifier, scope, period and current status can be published alongside it.
ZoikoSuite does not provide legal, tax, accounting, audit, employment or other regulated professional advice. Software support for a compliance process is distinct from advice about what the law requires of you.
No percentages, savings, pass rates or risk-reduction figures are published, because none has verified evidence behind it.
Security Overview
Owns security control depth: zero trust, identity, encryption, isolation, telemetry and incident response.
Evidence Architecture
Owns evidence lineage depth. This page shows the six layers in summary only.
Data Residency
Owns residency depth by lifecycle stage and deployment option.
Privacy Architecture
Owns privacy control depth: classification, purpose, access scope and retention.
Certifications
Owns independent assurance. Will carry verifier, scope, period and status when any exists.
Policies
Owns authoritative policy texts, DPA and subprocessor list.
Trust Center
The hub, with the nine-status claim legend and the full destination index.
Route diligence to the evidence that exists
Controlled-access evidence is released under NDA, scoped to your deployment. A review that returns "not available" is still a successful review.
- Completed security questionnaire — scoped to your deployment
- Architecture brief — zero trust, identity, isolation, telemetry
- Penetration test summary — under NDA, with scope and date
- Remediation targets — severity-based internal SLAs
- Key custody options — eligibility for your deployment and region
- Gap statement — what is not available, stated directly
Request security review
Enough to scope a response, nothing more.
Bring the question your questionnaire cannot answer
Most security questionnaires ask whether a control exists. The more useful question is which deployment it applies to, who holds the key, and what happens when it fails. Those answers need your context, not a generic pack.
No certification, attestation, detection guarantee, notification window or availability commitment is made outside an approved commercial document.
Talk to a solutions architect
Every section of this page was readable without it.
Certification, encryption, keys, testing and response
Direct first sentences, then qualified detail. Every answer is present in the page source.
No. Security framework readiness is not presented as certification, and no independent assurance exists to share. If your procurement process requires a SOC 2 report or ISO certificate as a gate, that gate cannot currently be met. Knowing so early is more useful than discovering it at contract stage.