Know which policy is
current, what it
governs, and what
changed.
Review ZoikoSuite policy governance through versioned records with ownership, approval, scope, effective dates, review status, change history, and controlled access to supporting evidence.

Six things every published policy must be true of.
Owned
Every policy has an accountable owner and defined approval authority.
Versioned
Current and superseded versions remain distinguishable and traceable.
Effective-dated
Published requirements show when they take effect and what they supersede.
Scoped
Applicability is defined by product, entity, deployment, jurisdiction, or audience.
Reviewed
Review status is visible; overdue review cannot look silently current.
Evidence-linked
Policies connect to controls and evidence without implying a document alone proves operation.
Public policy registry
The canonical public/restricted-disclosure index. If no record has been approved for publication, reviewers see an intentional empty state — never fictional content.

Required empty-state pattern
Policy record detail
An indexable detail page for public policies, or a deep-linked drawer for restricted
metadata. Procurement-critical fields are never hover-only.
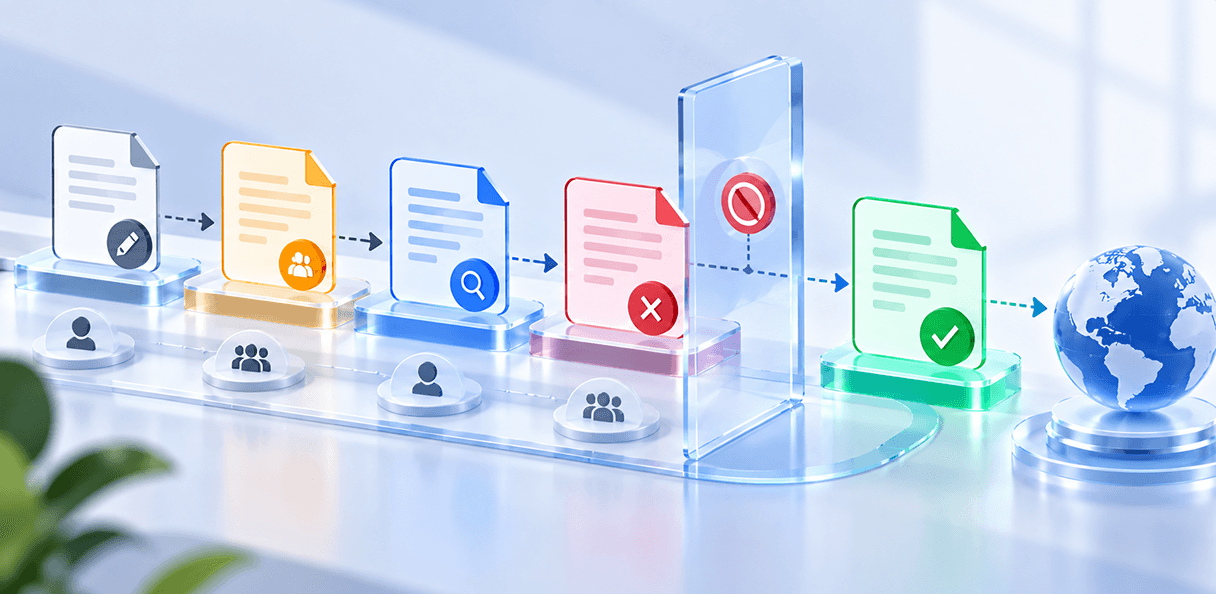
Policy lifecycle
A controlled state machine. Draft and internal review are described conceptually —
unpublished draft records never leak through the public site.
Scope before certainty
A policy can be approved and still not apply to every entity, deployment,
region, customer, employee, or workflow. Applicability is part of the policy
record, not a footnote.
Platform-wide or a named service/module.
Entity or entities subject to the policy.
Multi-tenant SaaS, dedicated, or sovereign/customer-
controlled.
Only where the policy differs by law, market, or location.
Employees, contractors, administrators, customers,
partners.
Explicit exclusions or local addenda, stated — not
implied.
Policy → control → evidence
Essential to avoid "we have a policy, therefore the control works." A published policy
proves an approved rule exists. The evidence trail shows whether the related
process operated. Independent assurance is shown separately.
Exceptions & risk acceptance
Policies without an exception model force shadow workarounds
or hide deviations. Exceptions are governed while sensitive records stay private.
Material deviations require documented scope, risk review, approval, compensating controls, and expiry.
A designated risk authority approves; the requester cannot self-approve where separation of duties requires it.
Every exception is time-bound. No permanent silent exception exists.
Named exceptions stay restricted by default. Active counts are published only when verified and contextualized.
Request restricted policy evidence
Some buyers need full policy documents or standards that shouldn't be public. This routes to a governed request path, not a generic contact form.
Policies vs. Legal documents
Trust policy summaries never replace or duplicate Legal. One canonical document owns each piece of content.
Governed by Policies (this page)
Governed by Legal (cross-linked, not duplicated)
Change history & notifications
Every version links to its predecessor and successor. Notifications appear only
where a real subscription service exists — never an implied promise to notify every
visitor.
Frequently asked questions
No. Some policies or standards are restricted because they contain security-sensitive or confidential operational detail. Public metadata and a controlled evidence request explain what's available.