Proof should be specific
enough to verify.
Review ZoikoSuite certifications, attestations, independent assessments, and readiness status with the scope, dates, issuer, evidence-access path, and limitations needed for enterprise diligence.
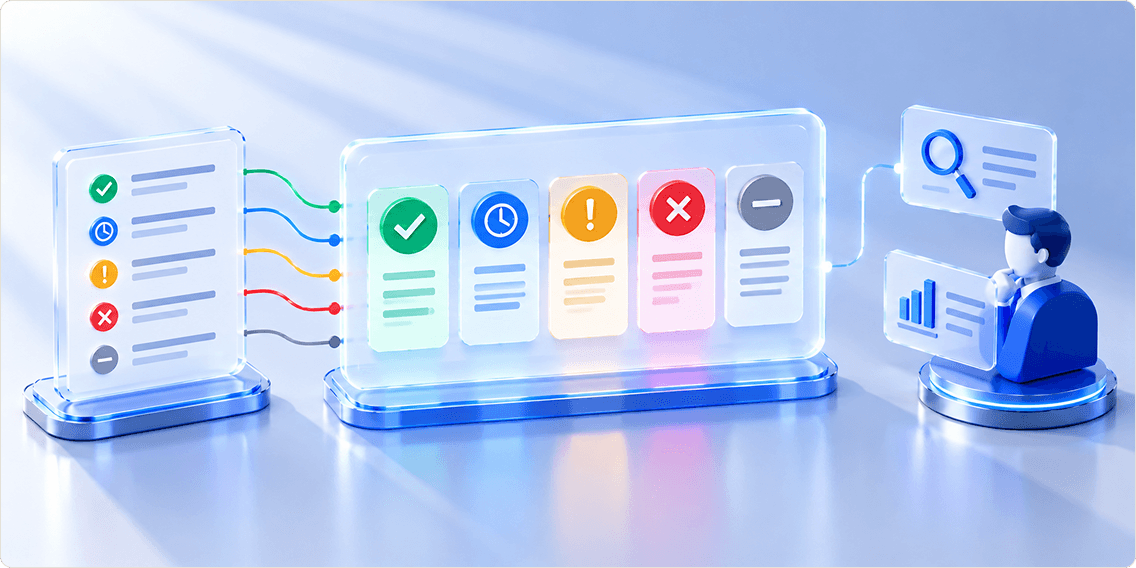
Current proof vs. readiness, in one scan.
Each card filters the registry below — no hidden mismatch between the summary and the detail.
The canonical public proof surface.
Empty and readiness states are valid and preferable to unsupported claims — records are never invented to fill the table.
| Assurance | Type | Status | Scope | Issuer / assessor | Evidence | Actions |
|---|---|---|---|---|---|---|
| ISO/IEC 27001 — Information Security Management | Readiness / alignment | Readiness | ZoikoSuite platform, production environment | Internal readiness | Readiness brief | |
| SOC 2 Type II — Trust Services Criteria | Readiness / alignment | Readiness | ZoikoSuite platform and supporting systems | Internal readiness | Readiness brief | |
| WCAG 2.2 AA — Accessibility | Readiness / alignment | In audit | ZoikoSuite web application | Internal testing | Internal testing notes | |
| ISO/IEC 42001 — AI Management System | Readiness / alignment | Planned | Not yet approved | Internal readiness | Governance policy |
A certification, an attestation, and a readiness item are not the same thing.
A badge without scope can mislead.
Enough boundary information to know whether an assurance actually applies to the service, legal entity, deployment, region, and period being evaluated.
| Scope dimension | Required treatment |
|---|---|
| Legal entity | Name the entity covered by the artifact. |
| Product / service | Specify ZoikoSuite platform or named modules/services. |
| Environment | Production, corporate environment, supporting systems, or specific service boundary. |
| Deployment | Multi-tenant, dedicated, single-tenant, sovereign/customer-controlled when covered. |
| Region / location | Stated only when the artifact itself defines it. |
| Period | Certificate validity or report observation period. |
| Criteria / categories | Criteria/categories included, stated explicitly. |
| Exclusions | Excluded products, controls, regions, or dependencies shown explicitly. |
| Customer responsibilities | Complementary user-entity controls shown where applicable and approved. |
Public where it can be. Controlled where it must be.
Request assurance evidence
Tell us what you need to validate — we route it to the right team and share only current approved evidence.
Honest progress, not a disguised certification badge.
External assurance outcomes are not controlled by marketing or product schedules — no future badge is shown as if issuance is guaranteed.
ISO/IEC 27001 — Information Security Management
SOC 2 Type II — Trust Services Criteria
WCAG 2.2 AA — Accessibility
ISO/IEC 42001 — AI Management System
Proofs that are not certifications, stated plainly.
| Validation type | Public detail | Related trust destination |
|---|---|---|
| Penetration testing | No independently approved summary published yet. | Security Overview |
| Vulnerability program review | No independent assessment published yet. | Security Overview |
| Accessibility assessment | Internal testing in progress; see readiness above. | Accessibility |
| Privacy assessment | No independent assessment published yet. | Privacy Architecture |
| AI governance assessment | No independent assessment published yet. | Responsible AI |
| Business continuity / resilience | No independent assessment published yet. | Security · System Status |
Mapping is useful for procurement. It is not certification.
A structured diligence entry point — not a gate on public truth.
Define requirement
Select required assurance types/frameworks and deployment.
Match current records
System shows current, readiness, not applicable, or unavailable — no hidden mismatch.
Review scope
Verify legal entity, service, region, deployment, dates, exclusions.
Request restricted evidence
Only relevant, currently approved artifacts are selectable.
Route review
Security/Compliance/Sales Engineering receives context; duplicate requests are linked.
Respond
Approved artifacts and explanatory notes shared through a governed channel.
Preserve evidence
Request, approvals, documents shared, version and timestamps logged where supported.
What each status means, before it ever applies.
This page proves assurance status. These pages prove the controls behind it.
Certifications & assurance questions
Current public posture is security framework readiness — not yet certified. This page lists only independently verified certifications or reports once issued and approved for publication.