Audit Committee
Make oversight easier to act on.
Give audit committees a clearer way to understand oversight priorities, follow evidence and management responses, and connect unresolved issues to accountable decisions—without confusing operational visibility with independent audit assurance.
Discuss evaluation context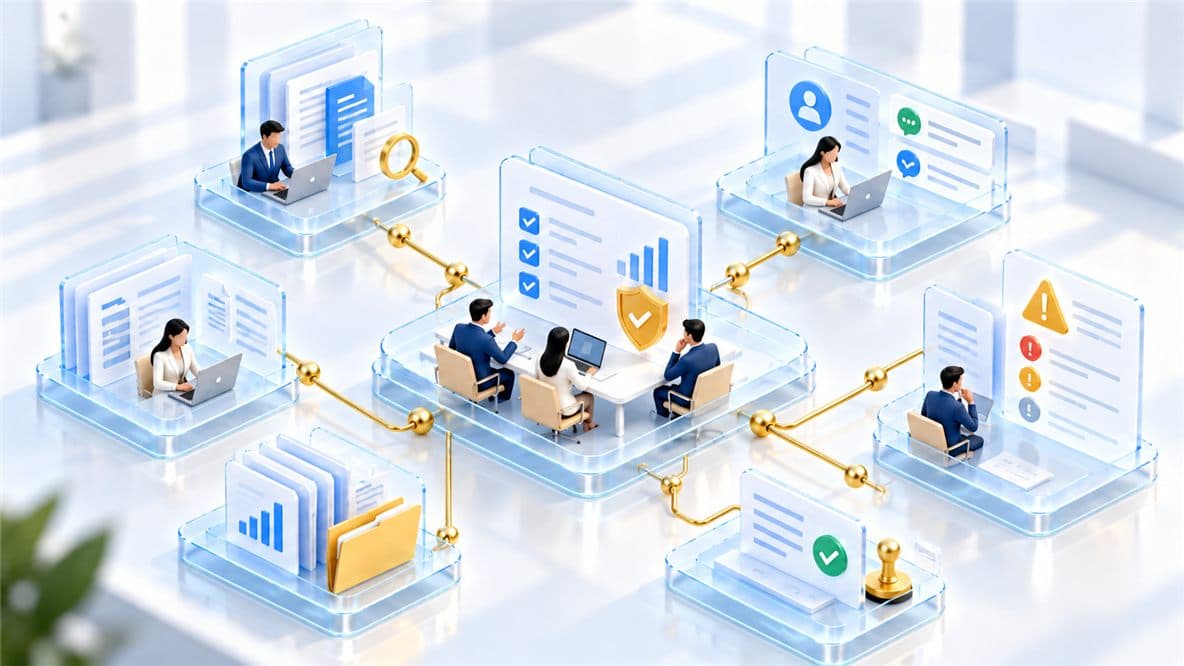
02 / Operating context
Explore the responsibilities behind the decision.
Decision value
Priorities, basis and accountability.
Recognize what needs attention
Unresolved issues and decision context without a false all-clear score.
Trace the basis for a position
Source, period, submitting party, reviewer and currentness travel together.
Keep the next action accountable
Management response and committee question remain distinct from independent closure.
Six oversight lenses
Ask the question. Inspect the basis.
Proposed modules explain a governance concept. They are not a live audit workflow.
AC-01Oversight Scope & Priorities
Proposed scope for this lens — a governance concept to discuss, not a live audit workflow.
AC-02Evidence & Provenance
Proposed scope for this lens — a governance concept to discuss, not a live audit workflow.
AC-03Findings, Exceptions & Risks
Proposed scope for this lens — a governance concept to discuss, not a live audit workflow.
AC-04Management Responses & Remediation
Proposed scope for this lens — a governance concept to discuss, not a live audit workflow.
AC-05Committee Questions & Decisions
Proposed scope for this lens — a governance concept to discuss, not a live audit workflow.
AC-06Reporting, Handoffs & Follow-Through
Proposed scope for this lens — a governance concept to discuss, not a live audit workflow.
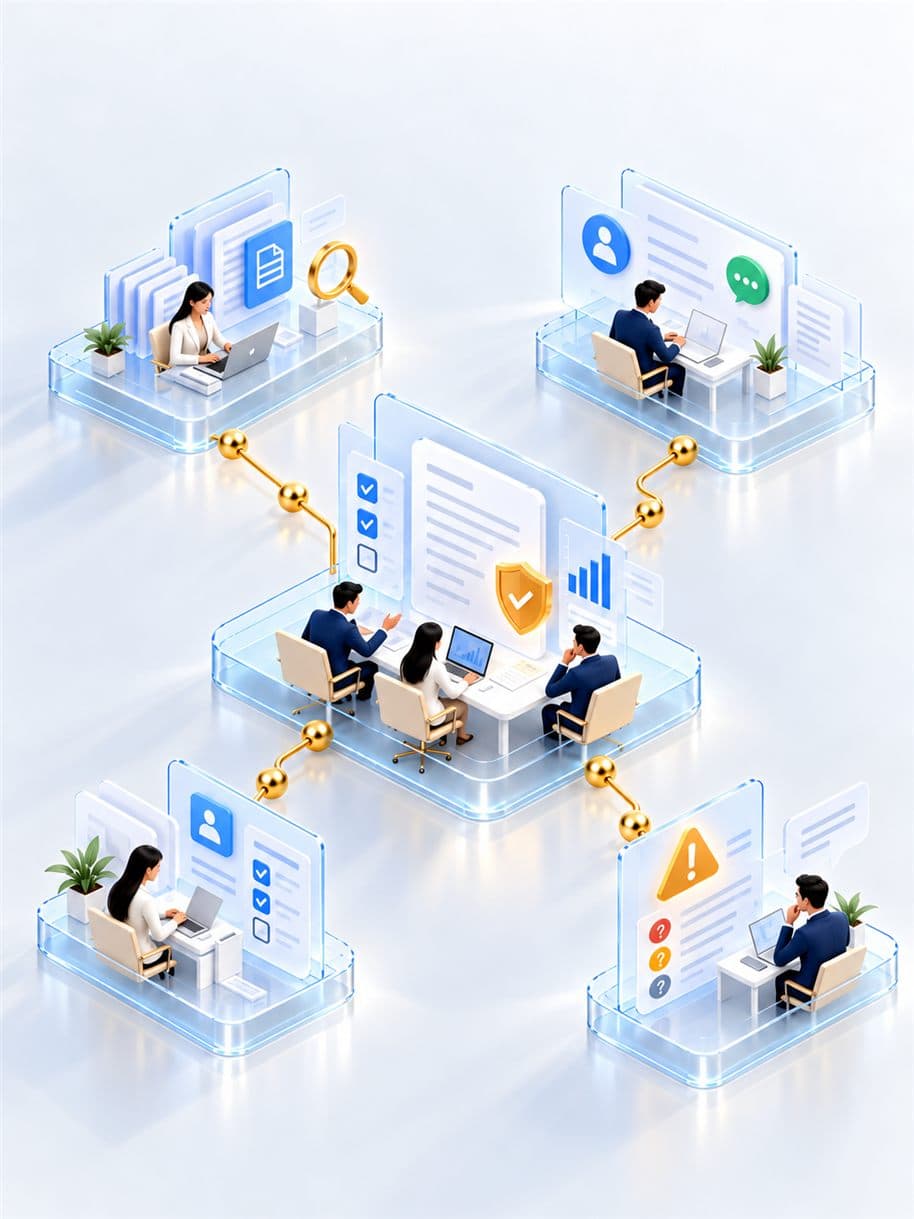
Illustrative evidence trail
Visibility is not assurance.
Keep management assertions, evidence references, reviewer findings and committee decisions separately attributed.
- OriginSynthetic access-review exception
- Management positionResponse/evidence submitted; not verified closure
- Reviewer dispositionPending; source/review date not established
- Committee questionWho confirms closure?
Separation of duties
Every role has a boundary.
- 01
Committee member
Authorized summaries and governed questions; cannot silently edit source evidence.
- 02
Committee chair
Agenda/priorities within actual charter; no administrative override inferred.
- 03
Management owner
Own responses and remediation; cannot independently attest own actions.
- 04
Internal audit liaison
Authorized findings/evidence with provenance separate from management.
- 05
Controller / Finance
Relevant finance response and authorization; cannot speak for committee.
- 06
Compliance / Risk
Assigned risk/control context; no legal sufficiency claim.
Oversight journey
Follow an exception without losing its context.
Step 1: Establish scope
Actual charter, period, source and accountable owner.
Step 2: Trace the issue
Origin, evidence and as-of status.
Step 3: Review management response
Planned action, target and supporting references.
Step 4: Identify review disposition
Independent findings remain separately sourced.
Step 5: Record next governance step
Committee question and decision source; no fake completion.
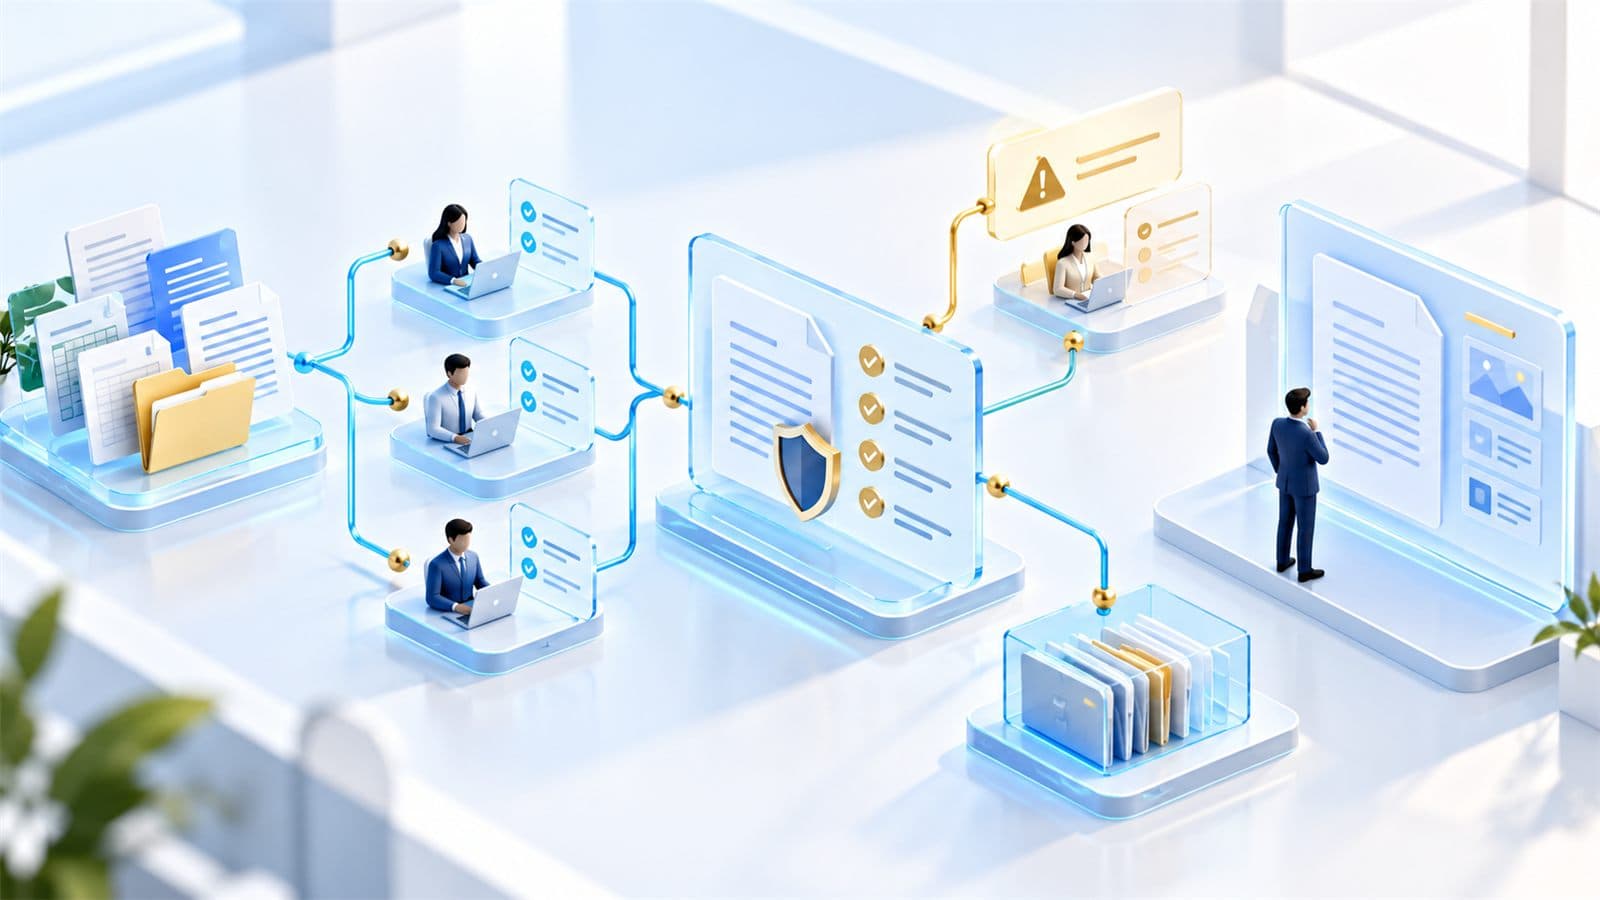
Trust & operating boundaries
Protect the record. Preserve the judgment.
- 01
Independent assurance
No audit opinion, independence or control-effectiveness claim from a conceptual overview.
- 02
Restricted material
Need-to-know, redaction and actual authorization before access; no leakage of private titles/content.
- 03
Stale or unavailable
Neutral source/review warnings; no green fallback or score.
- 04
Confirmed functionality
Integrations, upload/export, retention, immutable logs and board decisions need authorized evidence.
Related responsibilities
Connect roles without duplicating authority.
Controller
Financial management response and finance-owned context.
Compliance Ladder
Obligation/control ownership and risk context.
Tax Ladder
Tax-specific responsibilities where relevant.
Defining Properties
Shared governed-business principles; exact properties require product sign-off.
Buyer questions
Clarity before a briefing.
Does this replace internal or external audit?
No. This page is a conceptual overview for discussion — it makes no audit opinion, independence or control-effectiveness claim.
Is this a live product screenshot?
No. Imagery throughout this page is illustrative of the governance concept, not a screenshot of a live product.
Can management close its own finding?
No. Management can submit a response and remediation plan, but cannot independently attest to its own closure.
Does the page offer board voting or formal minutes?
No. This page does not provide board voting, formal minutes, or any other binding governance action.
Can it integrate with our systems?
Any integration, upload/export, retention or logging capability referenced here needs authorized evidence before it can be confirmed.
How is restricted evidence handled?
Through need-to-know access and redaction, with actual authorization required before access — no private titles or content are exposed.
Context before conversion
See how this applies to your own governance model.
Discuss the scope, responsibilities and evidence you need. This page illustrates a concept; it does not establish live product capability.
Review evaluation contextExecutive briefing / design preview
Start with your oversight question.
The briefing offer and operational request route remain unapproved in the source. This form is a local preview and does not book, send or store a request.