Turn obligations
into accountable,
reviewable work.
Explore a proposed governance approach for defining scope, coordinating owners, reviewing controls, resolving exceptions and preparing decision-ready evidence.
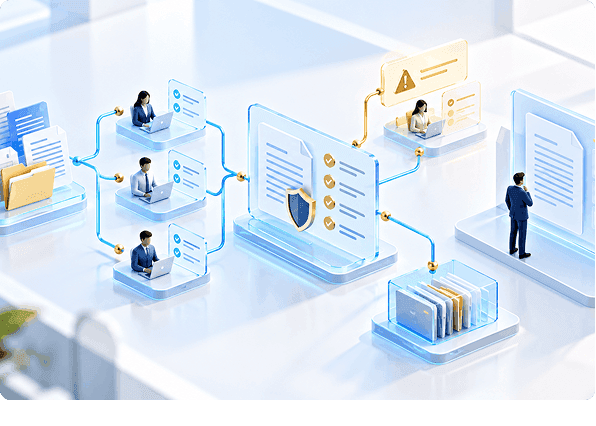
Explore the responsibilities behind the decision.
A progression of responsibilities.
Not a compliance score.
Understand the scope
Source version, entity and jurisdiction before interpreting applicability.
Coordinate accountability
Owners and reviewers remain separate, with clear next actions.
Prepare oversight
Dated evidence and unresolved decisions, without false all-clear signals.
Keep the source
beside the step.
Public examples are read-only concepts. Real administrative actions require verified product support and named authority.
A completed task
is not verified compliance.
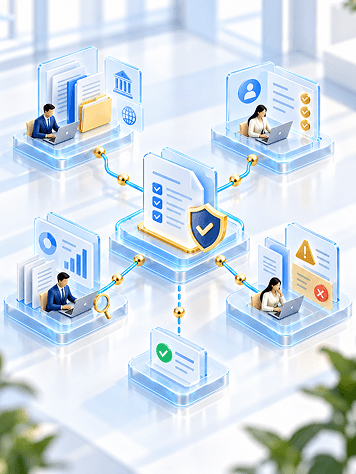
Keep obligation, assignment, control mapping, exception and evidence references separately owned and versioned.
Source and scope
Authority, entity, jurisdiction and effective version.
Owner and review
Preparation, approval and segregation remain distinct.
Evidence and oversight
Currentness, access and unresolved decision context.
Unknown stays unknown.
Not assessed / In review
Neutral task/review status, no certification implication.
Awaiting owner / Action required
Responsible next step, not regulatory conclusion.
Stale / Source unavailable
Date/version warning; no current or compliant fallback.
Restricted / Out of scope
Minimum disclosure and source-approved rationale; no hidden record leakage.
Different readers.
Different responsibilities.
Compliance & legal
Scope and interpretation require qualified approvers; no legal advice inferred.
Operations & IT
Assigned remediation and technical dependencies do not redefine legal determinations.
Audit & executive oversight
Approved high-level context, with restricted evidence protected.
Control owner
Update assigned work; no self-approval where segregation applies.
Board reader
Decision summary, not personnel-level evidence by default.
System administrator
Technical access configuration cannot override legal or audit decisions.
Governance clarity without overclaim.
No universal coverage
Countries, industries, obligations and integrations need confirmation.
No evidence guarantee
Immutability, audit readiness, exports and retention remain unverified.
Sensitive records
No actual organization records, raw evidence or personal data in the public page.
No automated assurance
Tracking and internal review never imply continuous compliance or certified standing.
One responsibility, one authoritative owner.
Tax Ladder
Tax-specific obligations and accountability remain distinct.
Controller
Finance controls and evidence stewardship.
Audit Committee
Independent oversight and challenge, not administrative editing.
CIO / CHRO / COO / Board
Role-specific context without duplicated state engines.
Defining Properties
Shared governed operations principles only when approved.
Know the limits before evaluating.
See how this applies to your own governance model.
Discuss the scope, responsibilities and evidence you need. This page illustrates a concept; it does not establish live product capability.
Start with a
governance question.
Demo offers, canonical route, privacy notice and operational form provider require approval. This local form sends/stores no data and books no demo.